Full security scans on every domain
Find what attackers see, before they do
Run a security scan on any domain in your portfolio in one click. Open-port scanning, TLS audits, OWASP web vulnerability checks, WordPress-specific scans, subdomain discovery on a full scan, and an AI summary of the findings, all from your dashboard.
Card not charged until your trial ends
01 · Why scan
Why running scans matters
If you manage more than a handful of domains, you can’t manually pentest each one every month. TLDTrack runs the heavy tooling for you, then summarises the findings in plain English.
See your real attack surface
CVE coverage without rule-writing
Plain-English findings
Track posture over time
02 · Coverage
What every scan covers
Each scan runs in an isolated Fargate container with industry-standard tooling. Nothing is shared between customers, nothing is cached.
Subdomain discovery
Port & service scan
TLS / SSL audit
Security headers
Tech fingerprinting
Nuclei vulnerability templates
WordPress-specific
OWASP web app scan
AI summary of findings
03 · Scan depths
Two scan depths
Quick baseline for routine checks; deeper active scan when you need a real audit.
Baseline · ~10 minutes
Passive & light-active scan
- Included on Starter, Pro and Agency
- Re-run any time, results stored against the domain
- Roughly 10 minutes from click to report
Full · an hour or more
Active OWASP web app scan
- Active scanning is intrusive: only run it on sites you own or have permission to test
- Recommended once per quarter per site
- Suggested IP allowlisting for sites behind strict WAFs
Security scans spend monitoring credits from your monthly pool, 2 credits for a baseline scan, 8 for a full deep scan, out of 250, 1,250 or 5,000 credits a month on Starter, Pro and Agency. Need more? Extra credit packs are available (100 for $32, 300 for $75, 750 for $150), and purchased credits never expire.
04 · Pricing
Simple, transparent pricing
Every paid plan starts with a 7-day free trial. Cancel during the trial and you won't be charged.
Free forever
Free
Monitor one site, free forever
$0/mo
1 website + 4 extra monitors
No credit card needed
- Uptime checks every 5 minutes
- Response time tracking
- Domain expiry alerts
- SSL certificate expiry alerts
- Email alerts
7 days free
Starter
For individuals & small portfolios
$11/mo
Up to 5 websites
250 monitoring credits / month
- Uptime, SSL, DNS & blacklist
- Content & visual change monitoring
- Accessibility (WCAG 2.2) monitoring
- Email health & renewal alerts
- PageSpeed & malware scanning
- Free WordPress plugin
- WHM & cPanel monitoring
- Bulk import & export
- Security, SEO & compliance scans
- AI integration (Claude & ChatGPT)
Most popular
Pro
For active managers & agencies
$29/mo
Up to 25 websites
1,250 monitoring credits / month
- Everything in Starter
- Up to 5 team members
- Client report builder
- AI search visibility
- Priority support
- Security, SEO & compliance scans
- AI integration (Claude & ChatGPT)
7 days free
Agency
For large portfolios & teams
$89/mo
Up to 100 websites
5,000 monitoring credits / month
- Everything in Pro
- Up to 20 team members
- Agency CRM & white-label reports
- Security, SEO & compliance scans
- Dedicated support
- AI integration (Claude & ChatGPT)
Bigger than 100 websites? Our Enterprise plan adds unlimited sites, custom data residency, an SLA, dedicated onboarding and custom integrations. Talk to us
*SMS alerts are an optional add-on on paid plans for UK mobile numbers, paid for with prepaid SMS credit packs. Prices exclude any applicable sales tax. Your card won't be charged during a paid-plan trial. Cancel anytime.
05 · Questions
Frequently asked questions
Is this a real penetration test?
Do I need permission to scan?
Will this trigger Cloudflare or other WAFs?
How long does a scan take?
Where does the scan run from?
Are findings stored?
Is there a free trial?
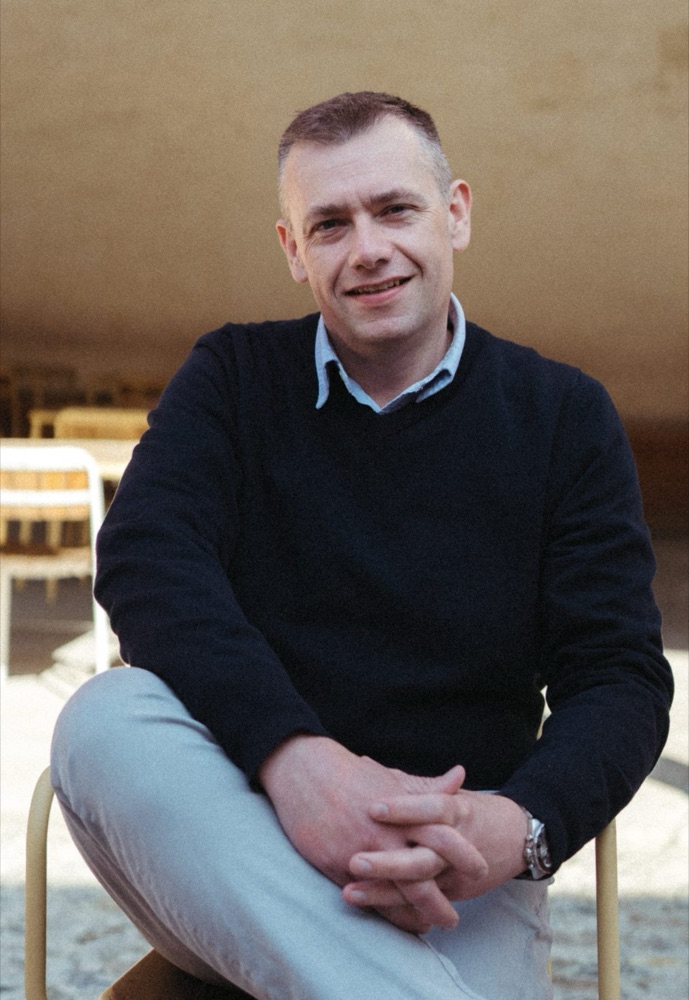
Mark Grice, founder of TLDTrack. Runs FullyCoded, a Cornwall web agency, and built this to keep 500+ client sites in front of him every day.
What happens next
Stop hoping the staging box is locked down
Do it yourself
Start your free trial
One click. Full scan. Plain-English report. Run it against every domain you manage, every quarter, without a security consultant on retainer.
Start your free trialTalk it through
Arrange a call with Mark
If you would rather talk through how this works across every site you look after, we can go through it together.
Book a call06 · Explore